Keycyte NCM — Network Configuration Management & Security Platform
Backing up is not enough
Most organisations back up their network configuration somehow. The problem isn't the backup — it's that the backup tells you nothing.
Who changed what, and when?
The files are there, but nobody reads the differences between them. After an outage, answering “what changed yesterday?” takes hours.
The rule base fills with junk
Years of shadowed, redundant and overly broad rules accumulate. Nobody knows which ones are safe to delete, so none of them are deleted.
Vulnerability tracking is manual
Copying firmware versions into a spreadsheet and comparing them against CVE lists by hand. At 40 devices, the job never finishes.
The data cannot leave
Cloud-based tools are unusable in regulated, defence or critical infrastructure environments.
One platform: back up, analyse, protect
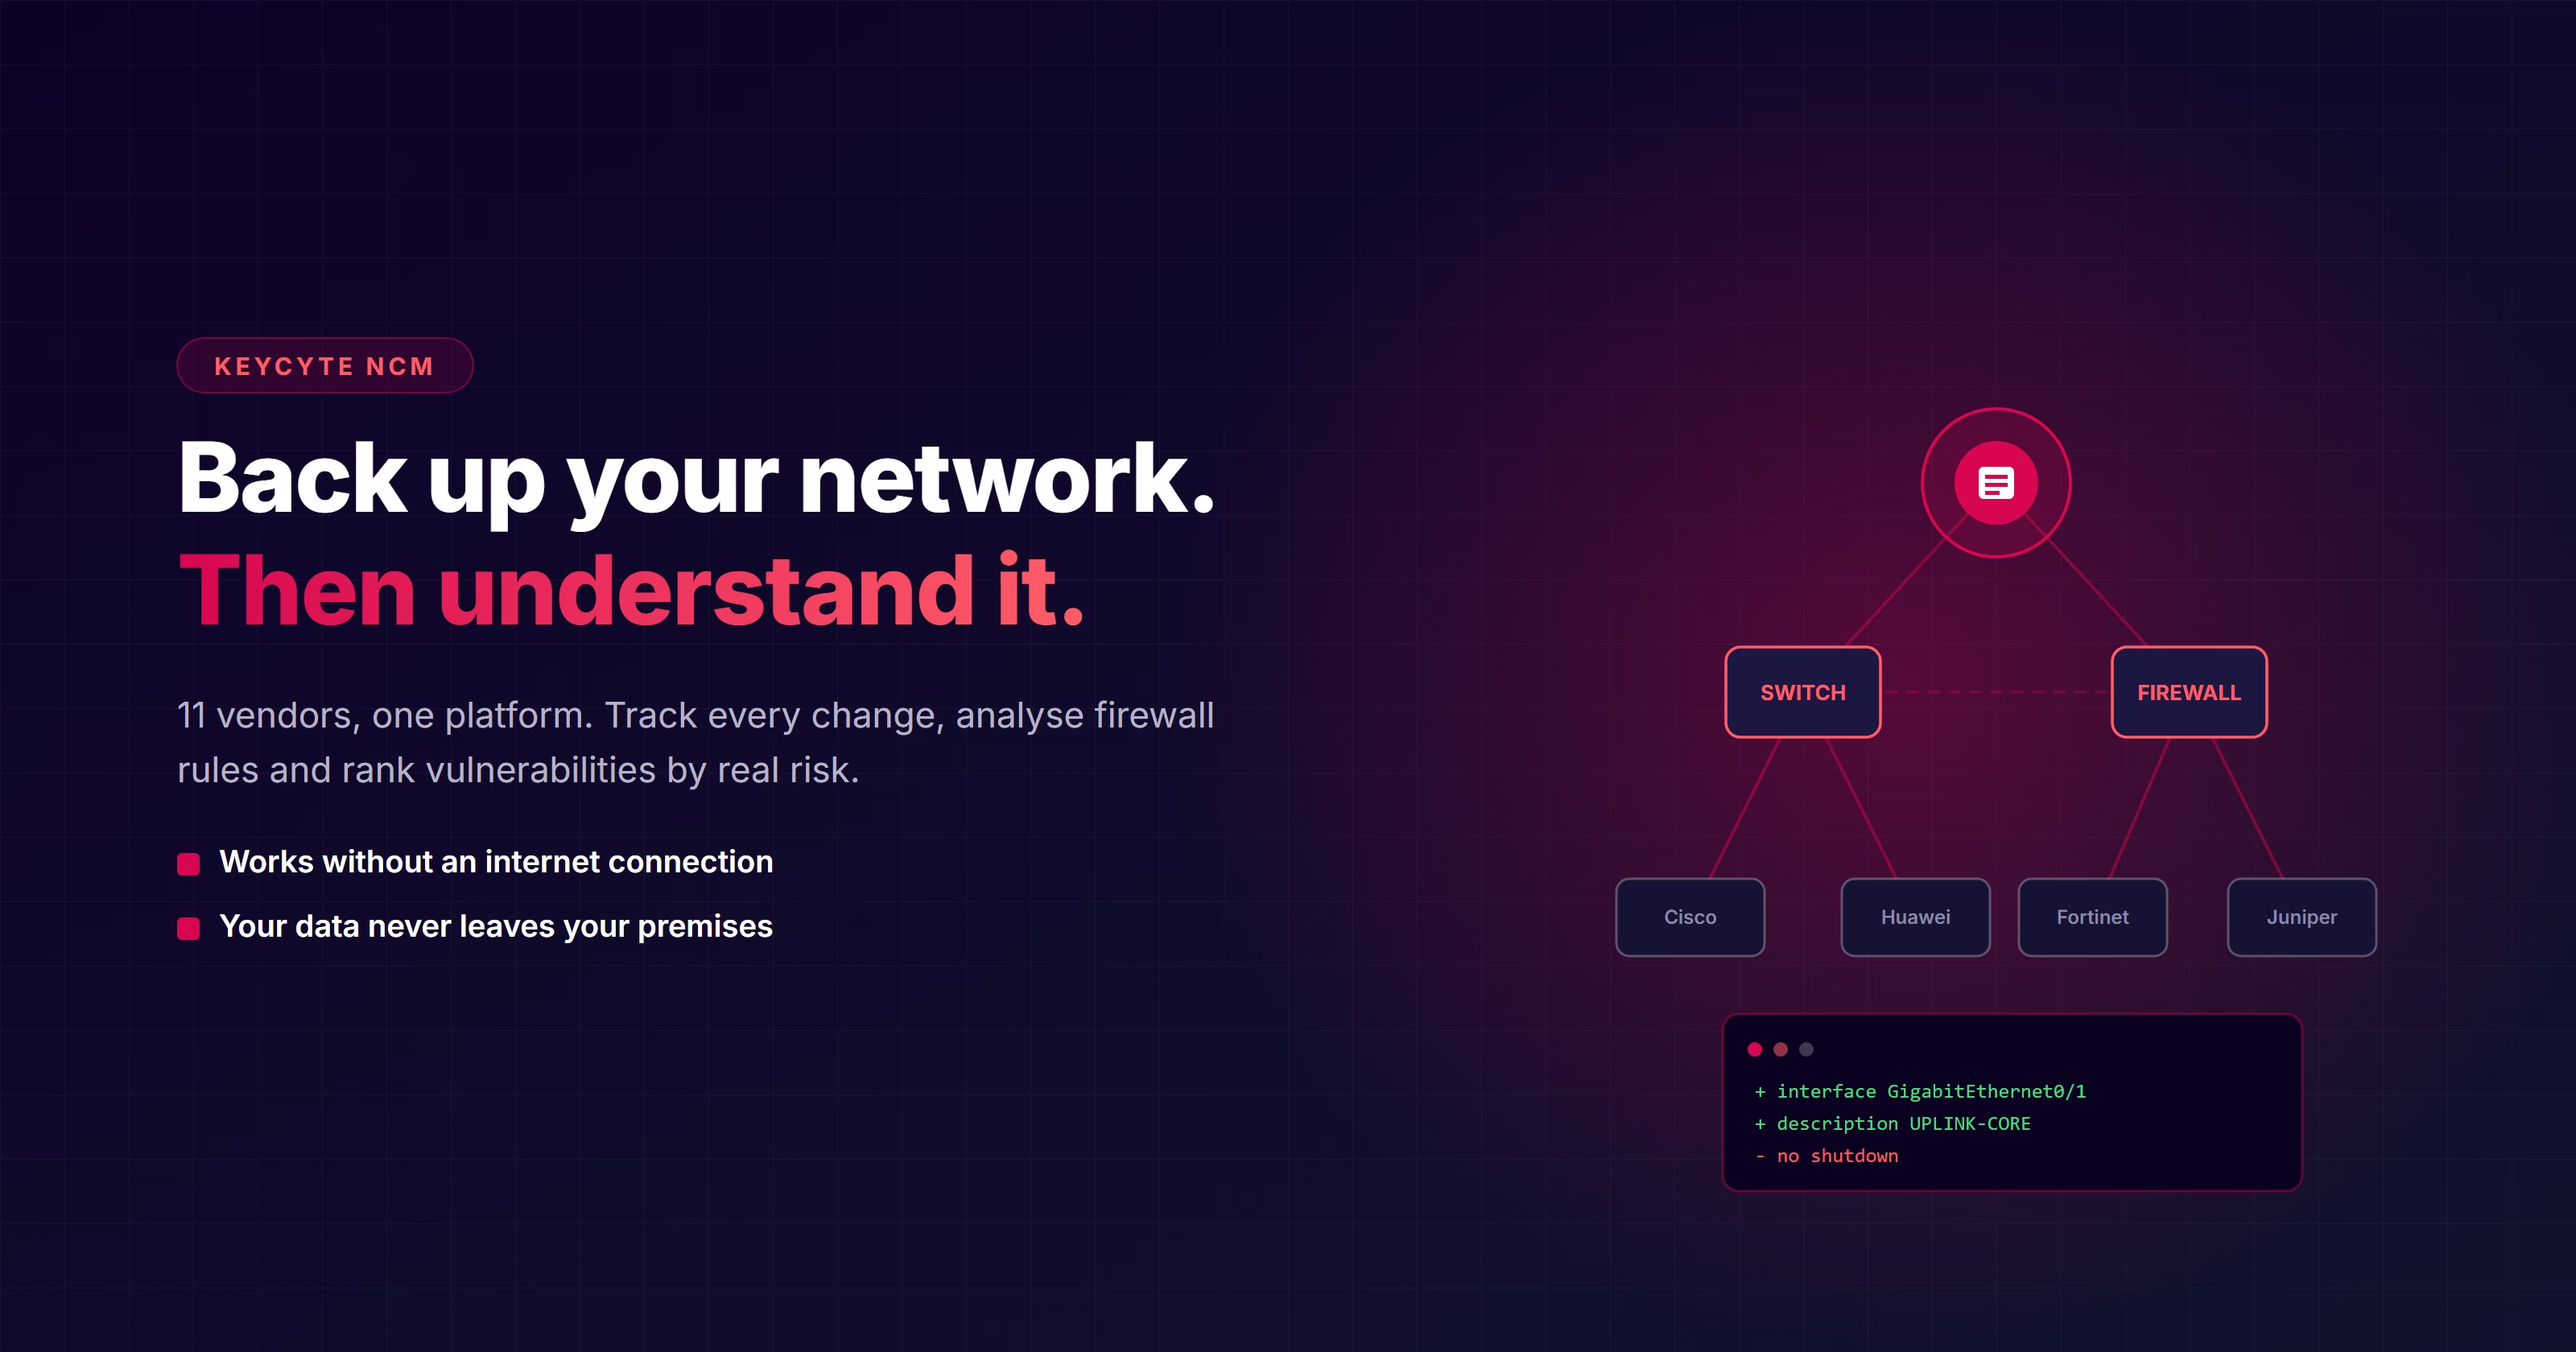
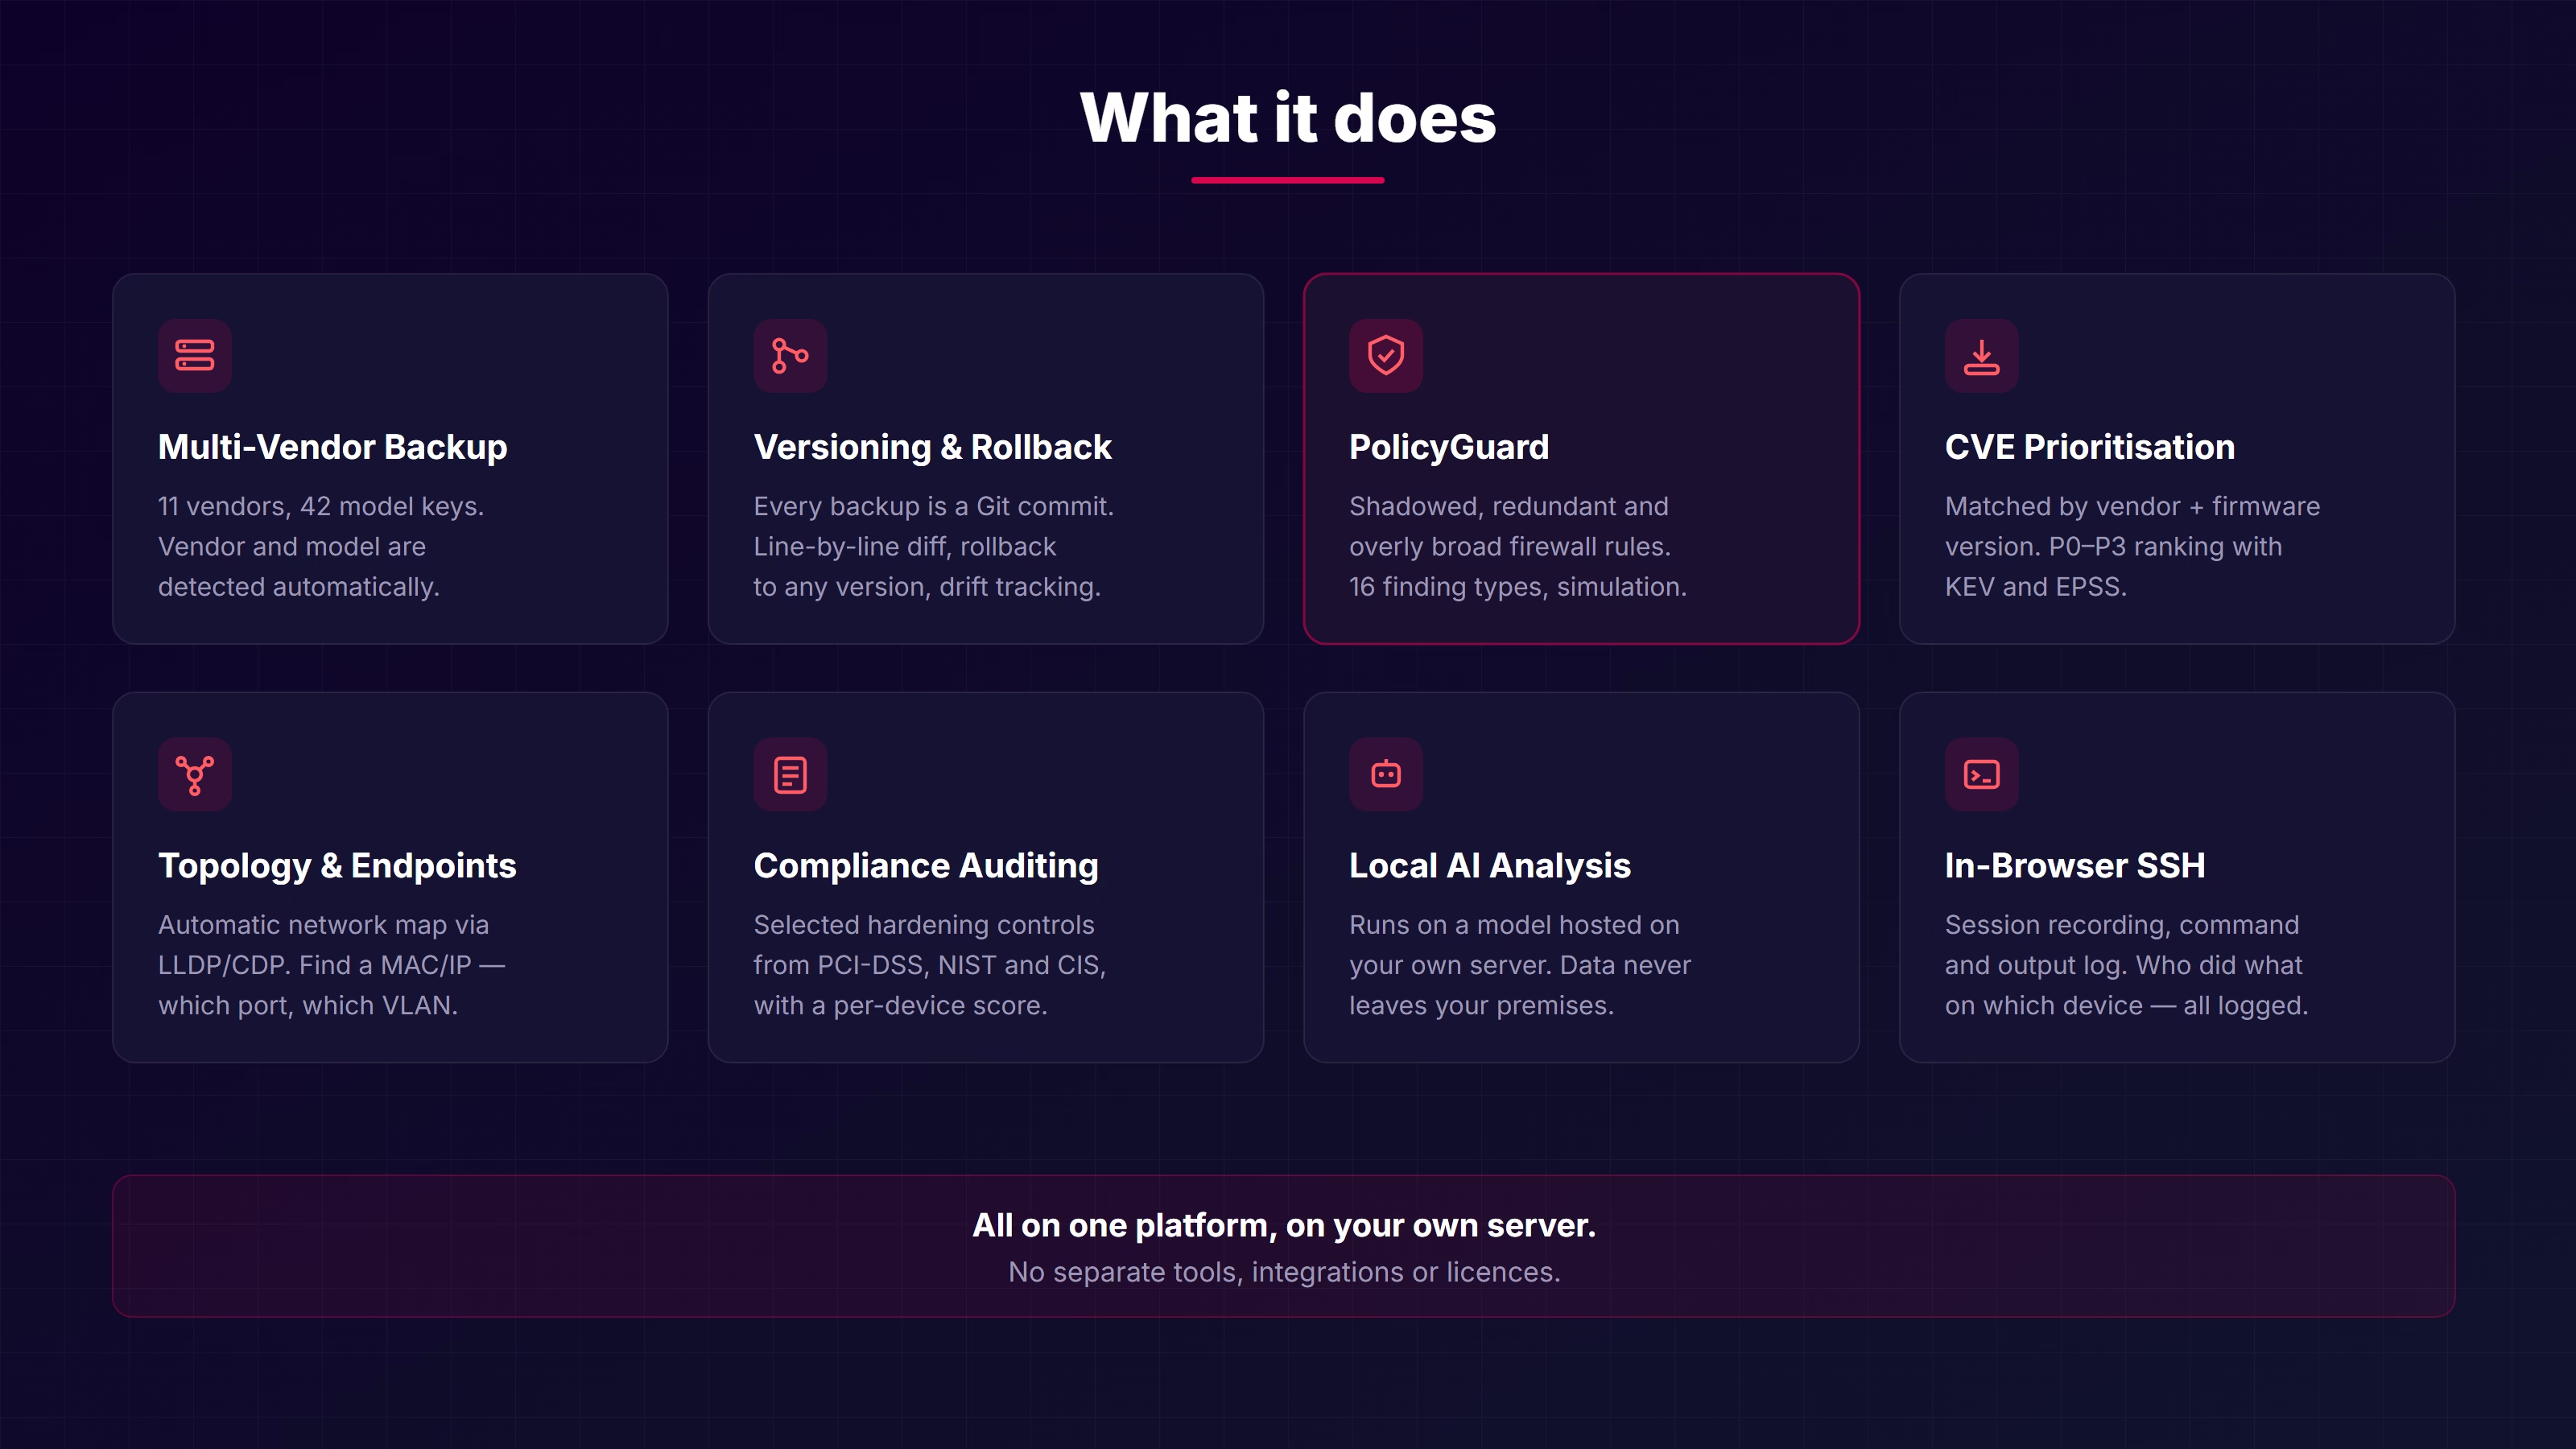
On top of the backup, Keycyte NCM adds security analysis, compliance auditing, vulnerability prioritisation, firewall policy analysis, topology discovery and local AI review.
11 vendors, one screen
Mixed networks are a fact of life. No separate tool per vendor is required.
| Vendor | Platforms |
|---|---|
| Cisco | IOS, IOS-XE, IOS-XR, NX-OS |
| Huawei | VRP + CE / AR / NE / AC / S57xx–S97xx |
| Juniper | JunOS (EX, MX, SRX, QFX) |
| Palo Alto | PAN-OS |
| Fortinet | FortiOS |
| Check Point | Gaia |
| Aruba | CX, AOS, ProCurve |
| Arista | EOS |
| Dell | OS10, OS9, OS6 |
| H3C | Comware |
| F5 | BIG-IP (TMOS) |
Additional depth on Huawei: VRP-specific compliance checks, runtime inventory collection and CVE matching narrowed by model-to-CPE family mapping.
Works without an internet connection
Installs on your own server and needs no outbound connectivity to operate. Everything, including AI analysis, is local.
On your own server
Docker Compose installation. No cloud requirement, no external service dependency.
Data stays in
AI inference runs on a local model. Your configurations are never sent to any external service.
Encrypted at rest
Device credentials and reference configurations are stored encrypted with AES-256-GCM.
Honest note: The one exception is the CVE database. Vulnerability scanning works offline, but the vulnerability data needs an internet window to be populated the first time. In fully isolated environments this data is transferred via an offline package.
We state plainly what is ready today
In security products, overstated certainty costs more than a missing feature. Know exactly what you are buying.
The product never presents what it does not know as “safe”. No data means no finding; no evidence means no accusation.
Frequently asked questions
We already use Oxidized / RANCID. What's different?
They take backups. Keycyte NCM treats the backup as a starting point and adds security analysis, vulnerability prioritisation, firewall policy analysis and compliance auditing on top.
Our network has no internet access. Can it be installed?
Yes. Everything, including local AI, works offline. Only the initial population of the vulnerability database requires an internet window or an offline data package.
Will it write to our devices?
Not by default. Configuration reading and backup are read-only. Remediation and template workflows are approval-gated and currently run in preview mode.
How does it relate to Keycyte PAM?
They are two separate products. PAM manages privileged access; NCM manages and analyses network configuration. They can be used together, but neither requires the other.
See it on your own network
Installation is possible in isolated environments; during the demo your network configuration does not leave your organisation.
Request a Demo Contact UsNCM manages configuration; Keycyte MON shows you the live network.
Keycyte Hotspot manages guest and shared internet access; who connected, when and from which IP — the record stays on your own server.